CVE-2026-52796Low· 3.5▾ SunlitGogs has DoS in rendering issue index pattern
Gogs has DoS in rendering issue index pattern
▾ Sunlit zone — Low / medium · no exploitation signal
Depth score19/ 100 · Minimal
impact 19.3 · likelihood 0.1 · exploitation 0
Proof of concept
Need a working PoC? Pro members can cast a request and our team develops one — it lands right here.
Published
Jun 22, 2026
Updated
Jun 22, 2026
CVSS
3.5
Vendor
gogs
Product
gogs.io/gogs
CWE
CWE-1336
Depth score
19 · Minimal
EPSS
0.28% · p21
Platforms
—
Source
GHSA
Vector
—
EPSS history
Exploit-prediction probability, daily snapshots since Jul 4.
Timeline
Disclosure to exploitation, from the record and what we observed since indexing it.
- Published
Disclosed via GHSA
- EPSS first tracked
0.3%
Affected
- gogs.io/gogs <= 0.14.2
Patched in
- gogs.io/gogs 0.14.3
Full technical detail▾
Overview
Summary
Special template of issue index pattern may cause panic.
Details
in internal/markup/markup.go
link = fmt.Sprintf(`<a href="%s">%s</a>`, com.Expand(metas["format"], metas), m)
Issue index pattern is rendered to link with com.Expand.
However, com.Expand is not safe.
i = strings.Index(template, "}")
if s, ok := match[template[:i]]; ok {
when { is found but } not found, i comes to 1, template[:-1] will be called, and then panicked
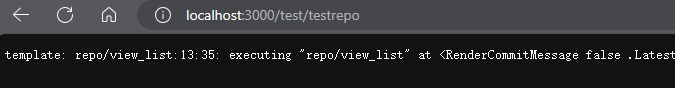
finally, all pages than contains issue index are unavailable.
PoC
- set issue index pattern as follow
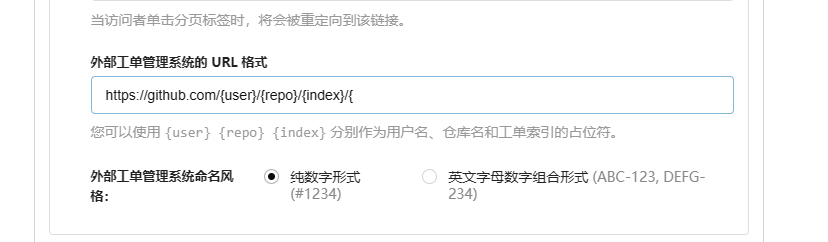
- add a commit which point to an issue in its msg
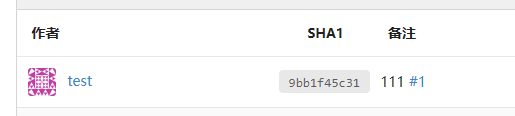
using #1 above
Impact
DoS that cause part of pages of the specify repo unavailable.
Affected packages
gogs.io/gogs <= 0.14.2
Remediation
Upgrade to a patched release:
gogs.io/gogs 0.14.3
References
Related vulnerabilities
Connected by shared product, vendor, weakness, or advisory.
CVE-2025-64719Medium· 4.9Gogs has a Denial of Service in repository/wiki file listing web pages
same productshared advisoryCVE-2026-25119HighGogs has an Authentication Bypass via Unvalidated Reverse Proxy Headers
same productshared advisoryCVE-2026-52798High· 8.9Gogs has Stored XSS in `.ipynb` Preview
same productshared advisoryCVE-2026-52799High· 7.5Gogs Missing Authorization in Attachment Download
same productshared advisoryCVE-2026-52800High· 8.8Gogs Vulnerable to CSRF Leading to Organization Owner Takeover
same productshared advisoryCVE-2026-52801High· 8.1Gogs has the ability to import local repositories via Mirror Settings
same productshared advisory
#ghsa#go